
Secure access to everything your organisation depends on
We design, implement and improve identity environments built around Microsoft Entra - helping you protect users, applications, workloads and privileged access without creating unnecessary friction.
Identity architecture • Zero Trust access • Identity governance • Workload identity
Identity has become your security control plane
Your organisation no longer operates behind a single network perimeter. People, partners, applications and automated workloads need access to resources across cloud, SaaS and hybrid environments.
As that environment grows, identity controls can become fragmented. Permissions accumulate, policies overlap and accounts remain active long after they are needed.
Privileged access
Administrative rights are broader, more permanent or less visible than they should be.
Inconsistent controls
MFA and Conditional Access exist, but are not applied consistently across users, applications and risk scenarios.
Identity lifecycle gaps
Access is not always granted, changed or removed when people join, move through or leave the organisation.
AI agents & workload identities
Service principals, managed identities, automation accounts and AI agents can hold powerful permissions without clear ownership or review.
The result is greater security exposure, operational friction and difficulty demonstrating that access remains appropriate.
Identity needs to be deliberately engineered and continuously governed - not allowed to accumulate.
OUR IDENTITY CAPABILITIES
Build identity controls that work across your organisation
We help you establish the architecture, controls and governance needed to manage access securely - from initial strategy and design through to implementation and ongoing improvement.
Identity architecture and modernisation
Create a secure, scalable identity foundation aligned with your cloud and business strategy.
Microsoft Entra (previously Azure Active Directory) tenant and identity architecture
Role-based access control design
Legacy identity modernisation
Hybrid identity alignment
Authentication and federation strategy
Cross-organisational solutions for M&A, health and social care
Zero Trust and privileged access
Apply the right level of control to every access request while reducing permanent administrative privilege.
Conditional Access design and rationalisation
Privileged Identity Management
Risk-based access controls
Phishing-resistant authentication
Least-privilege and tiered administration
Identity governance and automation
Make access easier to manage, review and evidence throughout its lifecycle.
Joiner, mover and leaver processes
Entitlement management
Governance reporting and audit readiness
Access reviews and recertification
Approval and provisioning workflows
Application, workload and AI identity
Protect the non-human identities connecting applications, platforms and automated services.
Service principal and managed identity governance
Application registration and consent controls
Ownership, monitoring and lifecycle controls
AI agent and access controls
Credential, certificate and secret management
Need help identifying the right starting point?
IDENTITY BEYOND THE DIRECTORY
Identity must extend wherever your technology does
Identity can’t be treated as a standalone Microsoft 365 configuration exercise. It determines how people, applications and automated services interact with the platforms that run your organisation.
We integrate identity into the wider architecture so access remains secure as your cloud estate evolves.
Every connected environment.
One identity strategy.
Azure and cloud
Build identity, privileged access, and role design into landing zones and cloud operating models.
PLATFORMS
Data and AI
Control how people, applications, and AI agents access data, models, tools and services.
INTELLIGENCE
Microsoft Entra
Architecture • Access • Governance
IDENTITY BACKBONE
Applications
Connect SaaS, enterprise, and custom applications with appropriate federation, provisioning and access controls.
INTEGRATION
DevOps
Govern service connections, deployment identities, and secrets used by engineering teams and pipelines.
AUTOMATION
THE OUTCOME
Identity enables cloud adoption and innovation, without becoming the control gap that holds you back.
HOW WE WORK
From identity risk to sustainable control
We combine technical analysis with an understanding of how your organisation actually operates. The result is an identity environment that is secure, manageable and practical for the people responsible for it.
We establish your business priorities, current environment, risk profile and regulatory requirements.
Understand
We examine existing architecture, configurations, permissions, processes and governance controls.
Assess
We define the target architecture, control model and prioritised plan needed to close the most important gaps.
Design
We introduce and test agreed changes while managing risk, user impact and operational continuity.
Implement
We help you monitor effectiveness, govern access and adapt controls as your organisation changes.
Improve
Start where you need us. Engage Shaping Cloud for a focused piece of work or support across the complete identity lifecycle.
Find out where your identity risk sits
A PRACTICAL PLACE TO START
Our Identity & Access Health Check provides a structured assessment of the controls protecting your Microsoft Entra environment, Azure resources and connected applications.
We review identity structure and governance, privileged access, Conditional Access and MFA, application and AI identities, user lifecycle processes, access reviews, monitoring and reporting.
YOU’LL RECEIVE
✓
A clear identity-risk heatmap
Practical quick wins for the next 30-60 days
✓
A prioritised remediation plan
✓
✓
A strategic roadmap for longer-term improvement
You’ll leave with a clear view of the gaps that matter, what to address first and how to strengthen your identity controls without adding unnecessary complexity.
Standards-Based Federation
Enterprise identity cannot rely on proprietary integrations. Just because Entra is at your core, doesn’t mean you need be limited in your integration options.
We design and implement standards-based federation using:
OpenID Connect (OIDC)
SAML 2.0
SCIM for automated provisioning
This allows Microsoft Entra to operate as a secure identity backbone, while integrating cleanly with SaaS platforms, national (e.g. NHS Login, One Login) or third-party identity providers.
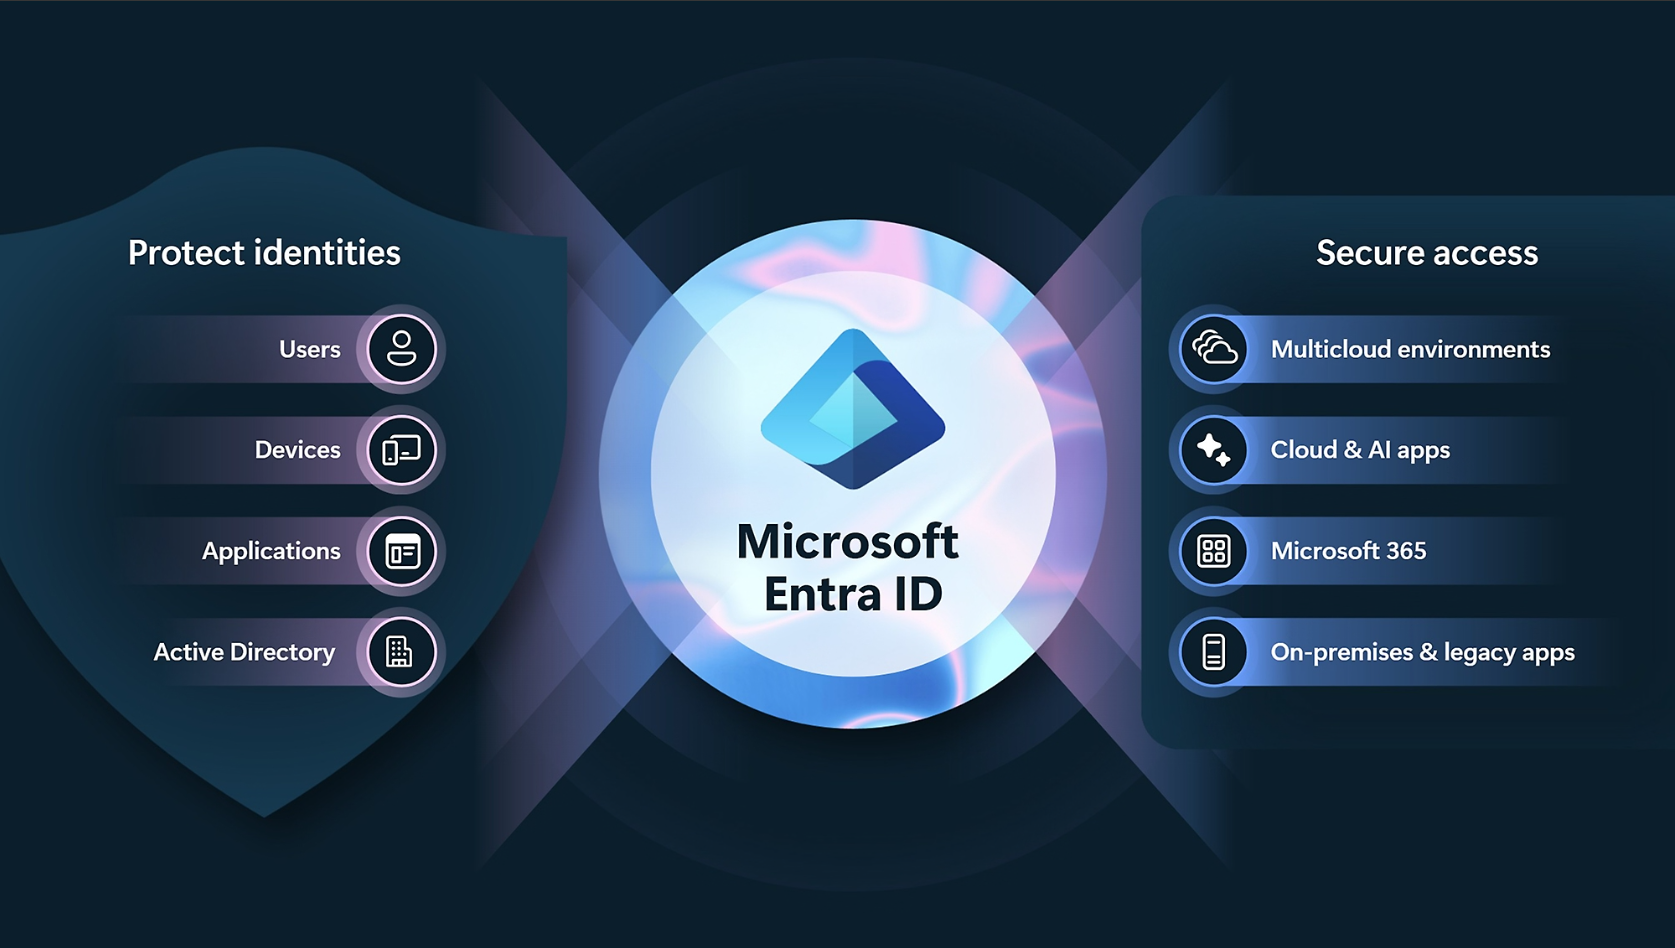
Where Identity Meets Cloud + AI
Most IDAM partners stop at M365.
Your data doesn’t.
Identity underpins:
Azure landing zones
DevOps pipelines
Data platforms (Microsoft Fabric)
AI workloads (including Azure OpenAI)
Secure API and integration architecture
Ongoing managed services governance
We integrate identity into cloud architecture from day one - not as an afterthought.
Identity Health Check
We provide a structured review covering:
Entra configuration baseline
MFA posture and conditional access design
Privileged access exposure and service principal risk
Identity governance gaps
RBAC misalignment
You receive:
Risk heatmap
Prioritised remediation plan
Quick wins (30-60 days)
Strategic identity roadmap